Glossary · Automotive
Development Process and Functional Safety
134 terms in the Automotive glossary, each with its one-line definition.
134 terms, A to Z
- Application Lifecycle Management ALM Software platform and practice that links requirements, changes, tests and releases so teams can prove what was built, tested and shipped.
- ASIL Decomposition Splitting one demanding safety requirement across two independent redundant parts, each developed to a lower and cheaper ASIL.
- ASPICE Capability Level Score from 0 to 5 that an Automotive SPICE assessment gives each process to show how mature and well managed it is.
- Association for Standardization of Automation and Measuring Systems ASAM German nonprofit body that writes shared formats and protocols for calibration, diagnostics, measurement data and simulation scenarios.
- Automatic Code Generation Producing production C or C++ code straight from a graphical control model with a tool instead of writing it by hand.
- Automotive Safety Integrity Level ASIL Rating from A to D that sets how rigorously a safety function must be developed, with D the strictest, based on harm, exposure and controllability.
- Automotive SPICE ASPICE Assessment model automakers use to judge how disciplined a supplier's system and software development processes are.
- Automotive SPICE for Cybersecurity Add-on to Automotive SPICE that assesses whether a supplier really carries out cybersecurity engineering in its projects.
- Back-to-Back Testing Feeding the same inputs to a model and its generated code and checking that both give matching outputs within tolerance.
- CANoe Vector Informatik tool for simulating, analyzing and testing ECUs and in-vehicle networks on a PC or HIL bench.
- Change Impact Analysis Check made before approving a change to find every requirement, design, test and safety argument it could affect.
- Chief Engineer Leader who owns a whole vehicle program's concept, targets and tradeoffs from early concept through launch.
- Common Cause Failure CCF Single root cause, such as a shared power supply or the same bug, that knocks out two supposedly redundant parts at once.
- Computational Fluid Dynamics CFD Computer simulation of air and liquid flow and heat transfer, used for drag, cooling, cabin climate and battery thermal design.
- Computer-Aided Engineering CAE Using simulation software to test and refine a vehicle design for crash, durability, noise, aero and heat before hardware exists.
- Configuration Management Labeling, versioning and controlling every requirement, model, code and calibration file so any release can be identified and rebuilt.
- Confirmation Measures Independent reviews, audits and an assessment that ISO 26262 requires to confirm the safety work was done properly.
- Cybersecurity Management System CSMS Company-wide processes and governance an automaker must certify under UN R155 to manage hacking risks over a vehicle's life.
- Dependent Failure Analysis DFA ISO 26262 analysis showing that supposedly independent parts cannot fail together from one cause or a spreading fault.
- Design Review Based on Failure Mode DRBFM Toyota-originated review that focuses on what changed in a design and asks how each change could cause a failure.
- Design Verification Plan and Report DVP&R Document listing every test a design must pass, with methods, samples, timing and results, to prove it meets requirements.
- Development Interface Agreement DIA Agreement between automaker and supplier on who performs which safety tasks and delivers which documents in shared development.
- Diagnostic Coverage DC Share of possible hardware faults that safety mechanisms detect or control, expressed as a percentage.
- Digital Mock-Up DMU Full 3D computer model of the vehicle assembled from all part CAD data to check fit, clearances and assembly access.
- Driving Intelligence Validation Platform DIVP Japanese research platform for virtually testing automated driving with physics-based camera, radar and lidar models.
- Durability Testing Testing that compresses a vehicle's full intended life into weeks or months of harsh driving, rig shaking and corrosion exposure.
- E-Gas Monitoring Concept Three-layer safety software pattern in which one layer runs the function, a second independently monitors it and a third checks the processor.
- Emergency Operation Tolerance Time Interval EOTTI Longest time a fail-operational system may run in degraded emergency mode after a fault before it must reach a safe state.
- End-to-End Protection E2E Safety mechanism that adds a checksum, counter and ID to critical messages so receivers can spot corruption, loss or delay.
- Error Correction Code ECC Extra stored bits that let hardware detect and automatically fix small memory or bus errors such as a flipped bit.
- Fail-Operational Design that keeps a system's essential function working after an internal failure until the vehicle reaches a safe condition.
- Fail-Safe Design that responds to a fault by switching off or falling back to a safe state, relying on the driver to take over.
- Failure in Time FIT Unit of electronic failure rate equal to one failure per billion device hours, used to add up hardware failure rates.
- Failure Mode and Effects Analysis FMEA Structured team exercise that asks how each part or process step could fail, what would happen and how to prevent or detect it.
- Failure Modes, Effects and Diagnostic Analysis FMEDA Quantitative FMEA for safety hardware that assigns failure rates to each failure mode and checks whether safety mechanisms catch it.
- Fault Detection Time Interval FDTI Time a safety mechanism needs to notice that a fault has occurred, budgeted within the window before harm can result.
- Fault Handling Time Interval FHTI Total time from a fault occurring to the system reaching a safe state or emergency mode, equal to detection plus reaction time.
- Fault Injection Testing Testing that deliberately corrupts memory, signals or wiring to prove that safety mechanisms detect faults and react in time.
- Fault Tolerant Time Interval FTTI Shortest time from a fault to a possible hazardous event if no safety mechanism acts, setting the deadline for detection and reaction.
- Fault Tree Analysis FTA Top-down analysis that starts from one undesired event and maps every combination of faults that could cause it using logic gates.
- Finite Element Analysis FEA Computer method that splits a structure into small elements to calculate how it bends, vibrates, heats or breaks under load.
- Freedom from Interference FFI ISO 26262 principle that a less critical function sharing a chip, memory or network must never corrupt or starve a more critical one.
- Functional Insufficiency Weakness in what a function was designed to do, with nothing broken, that can still cause dangerous behavior in certain situations.
- Functional Mock-up Interface FMI Open standard for packaging a simulation model from one tool so it runs inside another without sharing source code.
- Functional Safety FuSa Part of vehicle safety that depends on electronic systems working correctly and responding safely when they fail.
- Functional Safety Assessment Independent final evaluation of whether a product's functional safety is good enough to release.
- Functional Safety Concept FSC ISO 26262 document explaining at a logical level how a system will meet its safety goals and which parts carry each duty.
- Functional Safety Requirement FSR Safety requirement stating what a system must do to stay safe, without saying how it will be built.
- Functional, Logical and Concrete Scenarios Three levels of describing automated driving test situations, from a plain description to parameter ranges to exact values.
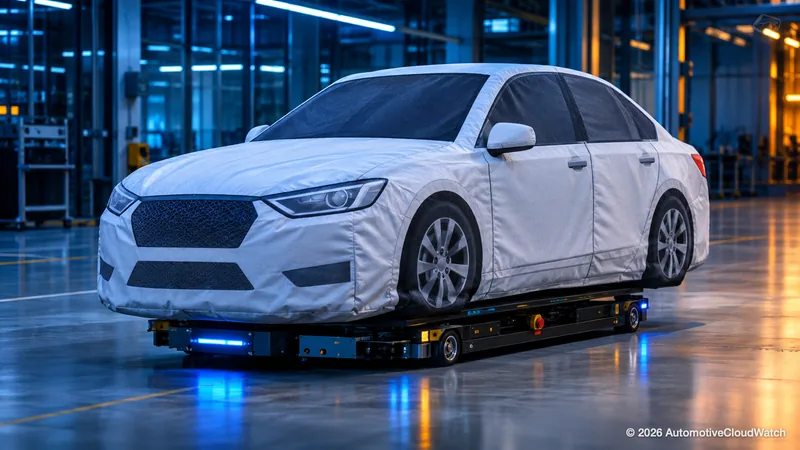 Global Vehicle Target GVT Foam soft-target car on a low robotic platform that sensors see as a real vehicle, used to test emergency braking safely.
- Graceful Degradation Strategy in which a system gives up features step by step after a fault instead of failing all at once.
- Hardware-in-the-Loop HIL Lab setup in which a real ECU is connected to a real-time computer that simulates the rest of the vehicle for automated testing.
- Hardware-Software Interface HSI Shared specification of how an ECU's hardware and software interact, including registers, memory, timing and diagnostics.
- Hazard Analysis and Risk Assessment HARA Early ISO 26262 study that rates how dangerous each possible malfunction would be and sets the ASILs and safety goals.
- Hazard and Operability Study HAZOP Structured brainstorming that applies guide words such as no, more, late or reverse to each function to find dangerous malfunctions.
- Hazardous Event Combination of a malfunction and a specific driving situation that could harm people, rated to set the needed safety rigor.
- IEC 61508 Original cross-industry standard for functional safety of electronic safety systems, parent of ISO 26262.
- ISO 24089 International standard for engineering software updates of road vehicles, over the air or in the workshop.
- ISO 26262 Main international standard for functional safety of electrical and electronic systems in road vehicles.
- ISO 34502 International standard on evaluating automated driving safety by testing against critical traffic scenarios.
- ISO/PAS 8800 ISO specification published in 2024 on the safety of artificial intelligence and machine learning in road vehicles.
- ISO/SAE 21434 International standard for cybersecurity engineering of road vehicles across their whole life.
- ISO/TS 5083 ISO technical specification published in 2025 on designing, verifying and validating Level 3 and higher automated driving systems.
- Item Definition First ISO 26262 document for a system, describing its function, interfaces, environment and assumptions to set the analysis boundary.
- Japan Automobile Research Institute JARI Japan's main independent automotive research and testing organization for safety, environment and automated driving.
- Lastenheft German term for the customer requirements document an automaker sends suppliers with a request for quotation.
- Latent Fault Hidden fault that causes no harm alone and goes unnoticed, but could lead to danger if a second fault occurs later.
- Latent Fault Metric LFM ISO 26262 percentage measure of how well a hardware design detects hidden faults that could combine with a later fault.
- Lockstep Core Pair of identical processor cores running the same instructions while hardware compares their results every cycle to catch faults.
- MISRA C Coding rules for safety-critical C that ban or restrict risky language features, required by most automakers.
- MISRA C++ 2023 MISRA coding rules for safety-critical C++17, now the reference C++ coding standard for automotive safety projects.
- Model-Based Design MBD Developing control software by building and simulating executable models first, then generating production code from them.
- Model-Based Systems Engineering MBSE Systems engineering that captures requirements, architecture and behavior in linked digital models instead of separate documents.
- Model-in-the-Loop MIL Testing a control algorithm model against a simulated plant entirely on a PC before any code is generated.
- Mule Early test vehicle that carries new systems under the body of an existing car so testing can start before the new body exists.
- Obeya Toyota practice of gathering a vehicle program's key people in one room covered with charts so decisions are made fast, face to face.
- Open Simulation Interface OSI ASAM data format for passing ground truth and sensor data between parts of a driving simulation from different vendors.
- OpenDRIVE Open file format describing road geometry, lanes, junctions, markings and signs for driving simulators.
- OpenSCENARIO Open standard describing how vehicles, cyclists and pedestrians move and react in a driving test scenario.
- Probabilistic Metric for Random Hardware Failures PMHF ISO 26262 measure of the probability per hour that random hardware faults violate a safety goal despite safety mechanisms.
- Processor-in-the-Loop PIL Running generated production code on the real target processor while the rest of the system is still simulated on a PC.
- Proven in Use ISO 26262 route for accepting an unchanged, long-fielded component as safe based on its field record instead of full redevelopment.
- Proving Ground Private test facility with high-speed ovals, handling tracks, rough roads and water baths for repeatable and secret vehicle testing.
- Quality Management Level QM ISO 26262 label for functions with low enough risk that normal quality processes suffice, ranking below ASIL A.
- Random Hardware Failure Hardware failure that occurs unpredictably during a part's life and is handled with failure rates and safety mechanisms.
- Rapid Control Prototyping RCP Running a new control algorithm on a prototyping computer in a real car or rig so it can be tuned before production code exists.
- Reasonably Foreseeable Misuse Predictable ways people use a car or feature other than intended, which safety standards require engineers to plan for.
- Requirements Management Process and tools for writing, reviewing, changing and tracking requirements across a vehicle program and its suppliers.
- Requirements Traceability Ability to follow links from each requirement to its source and to the design, code and tests that implement and verify it.
- Residual Bus Simulation Simulating the network messages of absent ECUs so one real ECU can be tested on a bench as if installed in a full car.
- Residual Risk Risk that remains after all planned safety measures are in place, which must be shown to be acceptable.
- RX Software Identification Number RXSWIN Identifier required by UN R156 that labels type-approval relevant software and must change when an update alters it.
- Safe State Operating mode with no unreasonable risk that a system moves to after detecting a fault, such as switching off or stopping.
- Safety Case Structured argument backed by evidence that a system is acceptably safe for its intended use, reviewed by assessors and regulators.
- Safety Element out of Context SEooC ISO 26262 approach for developing a safety component, such as a chip or OS, under documented assumptions without a specific vehicle.
- Safety Goal Top-level safety requirement stating what must be prevented to avoid a hazard, carrying the ASIL that every later requirement inherits.
- Safety Integrity Level Four-step IEC 61508 risk scale from SIL 1 to SIL 4, the industrial parent concept of the automotive ASIL.
- Safety Manual Supplier document for a safety component explaining its safety mechanisms, design assumptions and rules the integrator must follow.
- Safety Mechanism Hardware or software safeguard, such as ECC memory or a watchdog, that detects or controls a fault so the system stays safe.
- Safety of the Intended Functionality SOTIF Safety risk arising from a system's design limitations rather than from failures, such as a camera missing a pedestrian in glare.
- Safety Plan Project plan listing all safety activities, owners, schedule, deliverables and independent reviews for a system or component.
- SAKURA Project Japanese industry and government project building a real-world traffic scenario database and method for judging automated driving safety.
- Sample Phase Lettered maturity stage of supplier prototype parts, from early A-samples to D-samples made on the real production line.
- Scenario Database Searchable collection of driving situations used to test ADAS and automated driving in simulation and on the track.
- Scenario-Based Testing Validating ADAS and automated driving against chosen traffic situations rather than relying only on kilometers driven.
- Severity, Exposure and Controllability Three ratings given to each hazardous event in an ISO 26262 hazard analysis that together set its ASIL.
- Simulink MathWorks environment for modeling control systems as block diagrams, simulating them and generating code.
- Single-Point Fault Hardware fault that by itself directly violates a safety goal because no safety mechanism covers it.
- Single-Point Fault Metric SPFM ISO 26262 percentage measure of how well a hardware design covers faults that alone would violate a safety goal.
- Society of Automotive Engineers of Japan JSAE Japan's professional society for automotive engineers, which runs conferences, publishes research and develops JASO standards.
- Software Update Management System SUMS Company processes UN R156 requires automakers to certify for managing vehicle software updates safely and securely.
- Software-in-the-Loop SIL Testing compiled production code on a PC or server against a simulated vehicle, so thousands of tests can run automatically.
- SOTIF Scenario Areas ISO 21448 sorting of scenarios into known safe, known unsafe, unknown unsafe and unknown safe areas.
- Static Code Analysis Automated checking of source code without running it to find bugs, coding rule violations and security weaknesses.
- Strategic Innovation Promotion Program for Automated Driving SIP-adus Japanese Cabinet Office research program uniting industry, academia and ministries on automated driving and dynamic maps.
- Structural Coverage Measure of how much code the tests actually execute, such as the share of statements or branches run at least once.
- System-Theoretic Process Analysis STPA Hazard analysis that models a system as controllers and feedback loops to find unsafe control actions even without failures.
- Systematic Failure Failure caused by a mistake in specification, design, manufacturing or software that recurs whenever the same conditions occur.
- Target Cascading Breaking a vehicle's top-level targets such as weight, cost and efficiency into targets for each system and component.
- Teardown Analysis Taking apart a competitor's vehicle or component piece by piece to study its design, materials, manufacturing and cost.
- Technical Safety Concept TSC ISO 26262 document turning the functional safety concept into a concrete hardware and software design with specific safety mechanisms.
- Technical Safety Requirement Safety requirement stating how a functional safety requirement will be implemented in hardware or software.
- Threat Analysis and Risk Assessment TARA ISO/SAE 21434 study identifying assets, attack paths, attack feasibility and impact to decide which cyber protections are needed.
- Tool Qualification ISO 26262 process showing that development tools such as compilers and code generators will not introduce or miss errors.
- Triggering Condition Feature of a driving situation, such as low sun glare, that can expose a design weakness and lead to dangerous behavior.
- UL 4600 Goal-based safety standard requiring an evidence-backed safety case for autonomous products that operate without a human driver.
- UN Regulation No. 156 UN R156 UN vehicle regulation requiring automakers to manage software updates, including over the air, without undermining safety or approval.
- V-Model Development process drawn as a V, decomposing requirements down the left side and integrating and testing each level up the right.
- Validation Target Measurable goal, such as kilometers driven without a hazardous event, showing an automated function is safe enough.
- Variant Management Handling the many versions of functions and software across models, markets, trims and options built from a common base.
- Vehicle-in-the-Loop ViL Testing a real vehicle on a track or dynamometer while simulated traffic or sensor signals are fed into its systems.
- Verband der Automobilindustrie VDA German automotive industry association that also publishes globally used standards such as Automotive SPICE and VDA 6.3.
- Watchdog Timer that healthy software must reset regularly, restarting the ECU or forcing a safe state if the software freezes.
- Work Product Defined output of a development activity, such as a safety plan or test report, that serves as evidence the work was done.
Full entry for members
Every term has a full entry for members: the plain-words definition, the practitioner note and the typed links between terms.
ACW Automotive Glossary, edition 2026.11.1. The headword and one line are open to everyone.